TL;DR
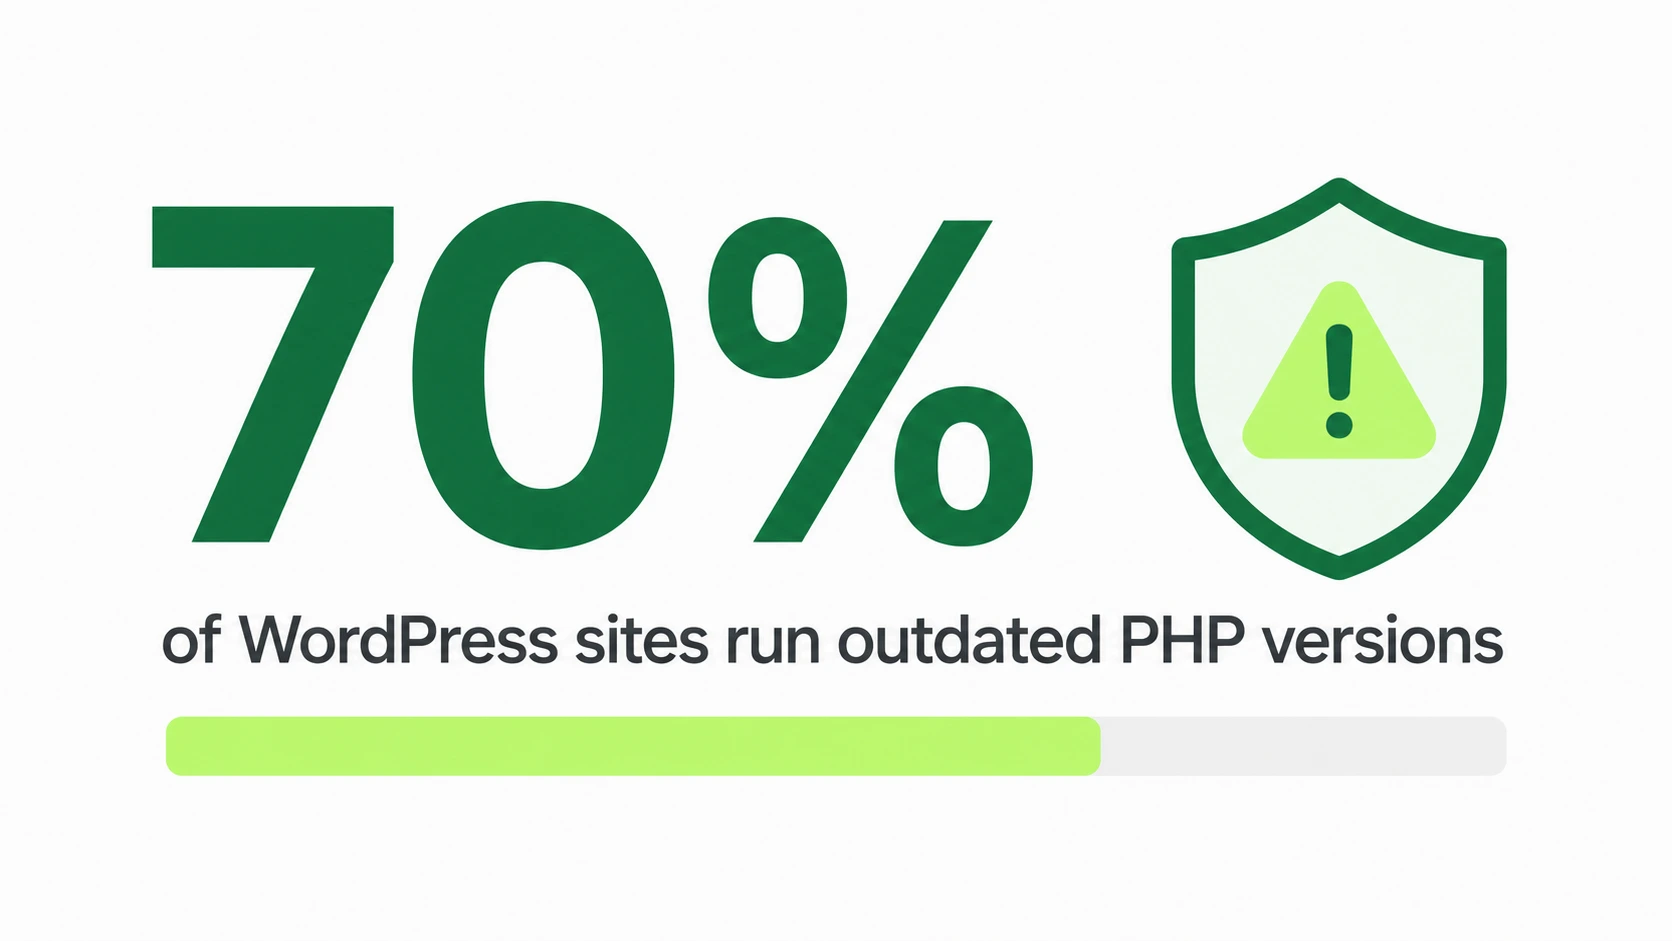
WordPress security breaches mostly come down to three things: outdated software (over 70% of WordPress sites run end-of-life PHP), weak passwords, and vulnerable plugins (91% of vulnerabilities originate there).
The core defense: keep everything updated, use strong passwords with two-factor authentication, install a security plugin like Wordfence or Sucuri, enable SSL, limit login attempts, and back up regularly. If your site is already showing signs of a hack, professional malware removal is faster and safer than troubleshooting it yourself.
Introduction
Why Securing Your WordPress is Critical?
WordPress is an open-source platform, which means it’s continuously being improved by developers worldwide. However, this also opens up opportunities for malicious actors.
Studies show that WordPress security breaches often come from weak passwords, old plugins, and unsafe themes.
1. Website vulnerabilities aren’t just a problem for large companies — small businesses and personal sites are equally at risk.
A 2026 Censys analysis found that over 70% of publicly visible WordPress sites are running outdated, end-of-life PHP versions — and only 14% are on the latest WordPress release. Outdated software is the single biggest factor putting WordPress sites at risk.
These weaknesses allow hackers to inject malware, steal sensitive information, and, in some cases, take over entire websites.
2. Outdated Themes and Plugins: Many users fail to update their WordPress themes and plugins regularly.
This is dangerous because developers often release updates to fix security loopholes. According to Patchstack’s 2026 security report, 91% of WordPress vulnerabilities originate in plugins, not WordPress core itself — running outdated versions makes your site vulnerable to known exploits that have often already been patched.
3. Weak Passwords: Another common problem is weak login credentials.
Many WordPress users still rely on simple passwords or default usernames like “admin.”
Hackers can easily exploit these with brute force attacks, trying different combinations until they gain access.
How Hackers and Malware Target WordPress?
- Brute Force Attacks: These attacks involve using automated tools to guess login credentials.
They target weak passwords and common usernames, and if successful, can lead to full access to your site.
- Phishing Attacks: Cybercriminals may trick your users into providing sensitive information by impersonating your website.
They often use phishing emails that look legitimate but direct users to malicious sites.
- Malware Infections: Malware can infect your WordPress website through outdated plugins, compromised files, or unverified themes.
Once inside, malware can steal data, display unwanted ads, redirect visitors to spam sites, or even crash your site entirely. If you suspect your site is already infected, a professional malware removal service can identify and clean the infection faster than working through it manually — especially if you’re not sure how deep it goes.
Essential Steps to Protect Your WordPress Website
Now that we’ve covered the potential risks, let’s dive into actionable steps to protect your WordPress from malware and hackers.
1. Keep WordPress Updated
Regularly updating your WordPress core, themes, and plugins is one of the most effective ways to close security loopholes.
Developers often release updates that include patches for vulnerabilities. Ignoring these updates leaves your site exposed.
To ensure your site is always up-to-date:
- Enable automatic updates for minor security releases.
- Regularly check your WordPress dashboard for major updates.
- Only use plugins and themes from reputable sources.

2. Use Strong Passwords and Two-Factor Authentication
Password security is your first line of defense against unauthorized access. Weak or reused passwords make it easy for hackers to gain access through brute force attacks.
- Use a mix of upper and lowercase letters, numbers, and symbols.
- Avoid common words or sequences (e.g., “password123”).
- Implement two-factor authentication (2FA) for an added layer of security. 2FA asks users for a second verification, like a code sent to their phone, making it much harder for hackers to get in.
3. Install a Security Plugin
- Monitor real-time traffic and block suspicious IP addresses.
- Scan your site regularly for malware and vulnerabilities.
- Implement a firewall for WordPress to block harmful traffic before it reaches your site.
4. Enable SSL and HTTPS
An SSL certificate keeps data safe by encrypting it between your site and users. This makes it harder for hackers to steal information like passwords or credit card details.
Your site will show “https://” in the URL and a padlock icon to show it is secure.
- Most hosting providers now offer free SSL certificates via services like Let’s Encrypt. Be sure to implement SSL across your entire website, especially on login pages and e-commerce checkouts.

5. Limit Login Attempts and Use CAPTCHA
One of the most common ways hackers gain access to WordPress sites is through brute force attacks.
Limiting the number of login attempts prevents hackers from repeatedly guessing credentials.
Plugins like Limit Login Attempts Reloaded allow you to block users after a set number of failed attempts.
- Add a CAPTCHA to your login form to ensure that a real person is trying to log in, not a bot.
6. Secure Your File Uploads
- Limit the file types that can be uploaded and use a plugin to scan uploaded files for malicious content.
Advanced Security Measures
1. Use a Web Application Firewall (WAF)
A Web Application Firewall (WAF) blocks harmful traffic before it reaches your site, acting as a shield between your site and the internet.
Services like Sucuri and Cloudflare offer WAF solutions tailored for WordPress.
2. Backup Your WordPress Website Regularly
No matter how secure your site is, there’s always a risk of being hacked.
Regular backups ensure that you can quickly restore your site to a previous, clean state if something goes wrong.
Use plugins like UpdraftPlus to automate daily backups, and store them securely offsite.
Common Signs of a Hacked WordPress Website
- Slow Site Performance: If your website suddenly becomes slow, it could mean there are harmful scripts or bots causing extra load on your server.
- Unusual User Activity or Logins: Look out for logins from unknown IP addresses or accounts you didn’t create. This can be a sign of unauthorized access.
- Changes to Website Content or Settings: If you see changes in your site’s content or settings, someone might have hacked your site.
Steps to Take After a WordPress Hack
- Scan for Malware: Use comprehensive security plugins such as Wordfence or Sucuri to perform a full scan of your website.
These tools can help identify malicious files, vulnerabilities, and unauthorized changes, and provide instructions for removing threats. If the infection is deep or keeps coming back after cleanup, that’s usually a sign it needs a professional, deeper cleanup rather than repeated plugin scans.
- Restore from Backup: If your site is badly damaged, using a recent backup can be the quickest way to fix it. Ensure that your backups are up-to-date and stored securely.
- Change Passwords: Quickly update passwords for all accounts that access your WordPress site, including FTP, database, and admin accounts.
Use strong, unique passwords and consider implementing two-factor authentication for added security.